> For the complete documentation index, see [llms.txt](https://docs.sonarsource.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.sonarsource.com/sonarqube-server/2025.4/instance-administration/authentication/http-header.md).
# HTTP header
Setting up the HTTP header authentication in your SonarQube Server instance.
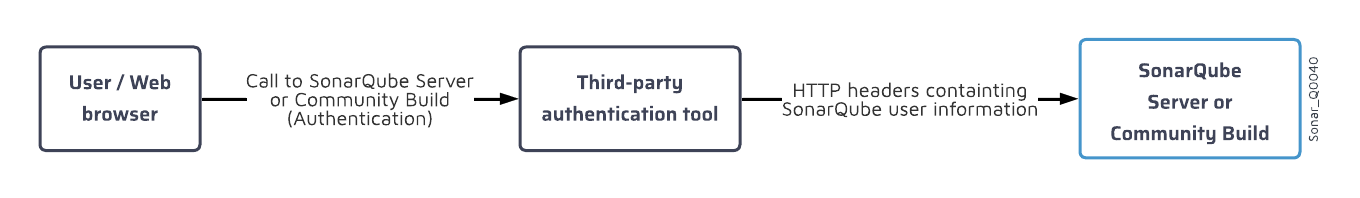
You can delegate user authentication to third-party systems (proxies/servers) using HTTP header authentication.
When this feature is activated, SonarQube Server expects that the authentication is handled prior to any query reaching the server. The tool that handles the authentication should:
* Intercept calls to the SonarQube Server.
* Take care of the authentication.
* Update the HTTP request header with the relevant SonarQube Server user information.
* Re-route the request to SonarQube Server with the appropriate header information.
{% hint style="warning" %}
**Securing the trust boundary is your responsibility.** When you enable HTTP header authentication, SonarQube Server trusts the configured identity headers without cryptographic verification. You must:
* Configure your proxy to authenticate every request and set these headers itself.
* Configure your proxy to strip or overwrite these headers on every incoming request, so a client cannot set them directly.
* Make sure SonarQube Server is not reachable directly, bypassing the proxy. Bind the web server to an interface that only the proxy can reach (`sonar.web.host=127.0.0.1` when the proxy runs on the same host) and restrict the port with a firewall. See [Reverse proxy and network security](/sonarqube-server/2025.4/server-installation/network-security/securing-behind-proxy.md).
If a request reaches SonarQube Server without going through the proxy, it can authenticate as any user managed through header authentication. The built-in `admin` account and other local accounts do not authenticate through these headers; they continue to sign in with their password.
{% endhint %}
All the parameters required to activate and configure this feature are available in SonarQube Server configuration file. See the `SSO AUTHENTICATION` section in `/conf/sonar.properties`.
Using HTTP header authentication is an easy way to integrate your SonarQube Server deployment with an in-house SSO implementation.
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation dynamically by asking a question.
Perform an HTTP GET request on the current page URL with the `ask` query parameter, and the optional `goal` query parameter:
```
GET https://docs.sonarsource.com/sonarqube-server/2025.4/instance-administration/authentication/http-header.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is optional and describes the broader end goal you are ultimately trying to accomplish on behalf of the user. GitBook uses it to tailor the answer towards what is most useful for that goal.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.