> For the complete documentation index, see [llms.txt](https://docs.sonarsource.com/llms.txt). Markdown versions of documentation pages are available by appending `.md` to page URLs; this page is available as [Markdown](https://docs.sonarsource.com/sonarqube-server/user-guide/security-alerts.md).
# Alerting on critical security findings with Security Alerts
In SonarQube Server 2026.5, Security Alerts notify teams when a new high-profile security finding is discovered that security teams need to review.
Security teams use Security Alerts to find and act on critical security findings. Administrators configure which groups receive notifications.
## What is a security alert?
Use security alerts to find the most critical issues that may require immediate remediation, such as:
* Public vulnerabilities known to be exploitable
* Malicious software used as a dependency
{% hint style="info" %}
Security Alerts currently cover **Blocker** dependency risks discovered by [SonarQube Advanced Security](/sonarqube-server/advanced-security/introduction.md), and require Advanced Security as a prerequisite.
Additional alert types will be added in future releases.
{% endhint %}
## How to view current alerts
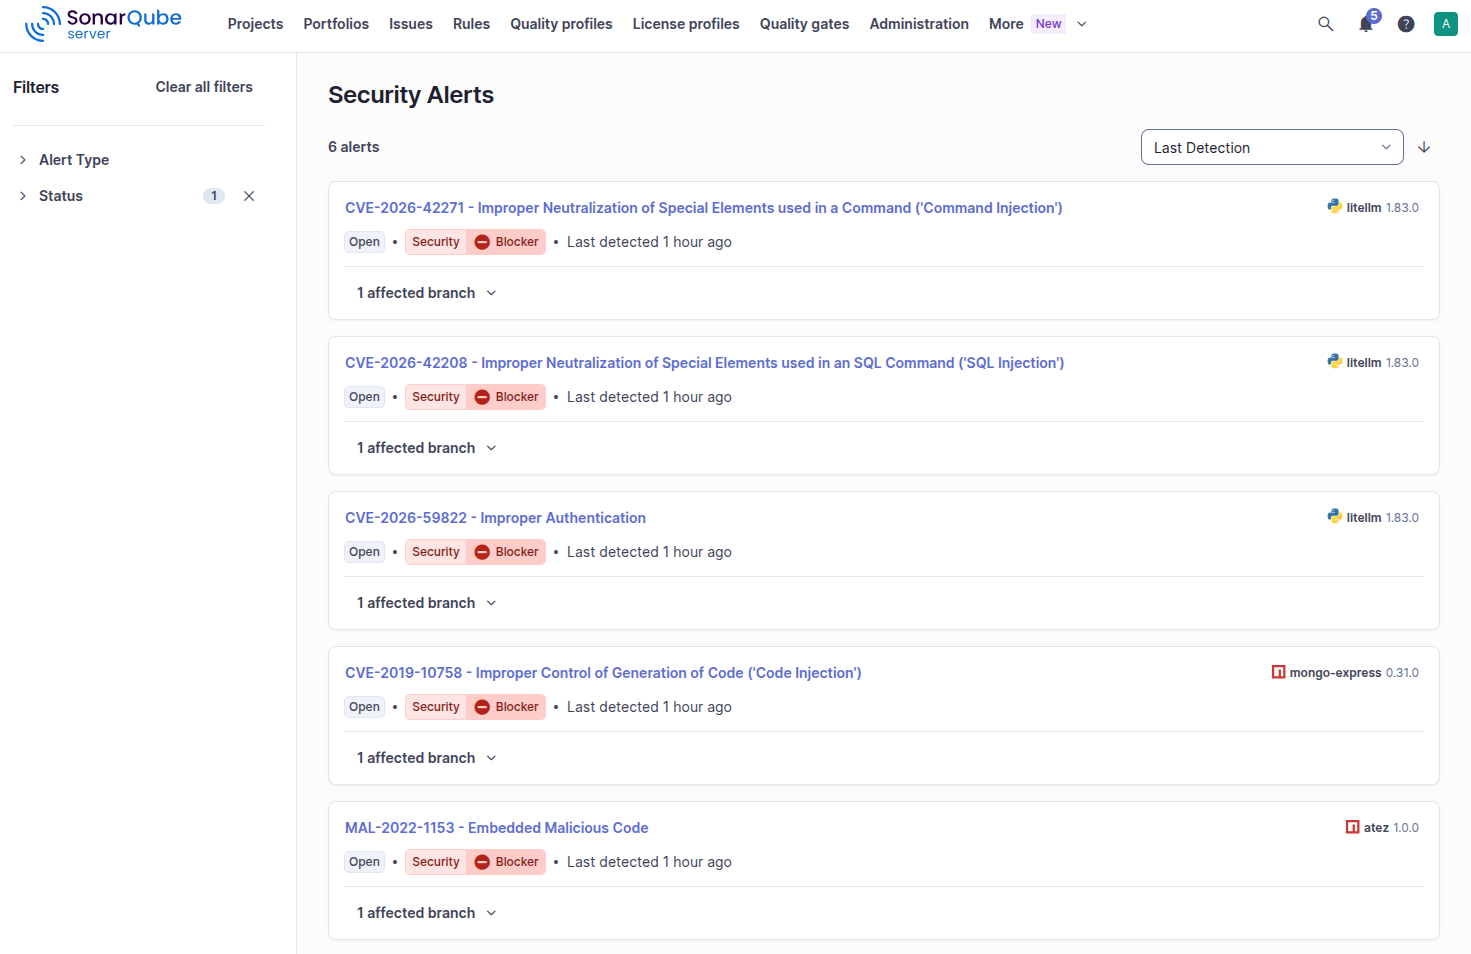
View security alerts in the top-level **Security Alerts** menu, available under the "More" section of the menu.
You can see alerts for any projects whose dependency risks you can view. If you have the **Administer System** permission, you can see all alerts.
Filter alerts by type (currently only dependency risks) and status. A risk is "Open" if the underlying issue or risk is still present in any branch analyzed by SonarQube. An alert is automatically "Resolved" when the underlying issue or risk is resolved on all branches. Each risk gives details of the risk, and a list of every branch in every project where the risk is present.
Select a risk to view more details on the risk and an expanded summary of how it affects each branch in each project where it is present. Select **View risk details** to see the risk in the context of the specific branch analysis of the affected project.
{% hint style="info" %}
Alerts are resolved when the risk is removed, or it is changed to a state such as **Safe**.
{% endhint %}
## Get notified of newly detected critical findings
Administrators can configure notifications so security teams are alerted when a new critical finding is detected.
To configure notifications:
1. Go to **Administration** > **Security** > **Groups**.
2. Choose the group you would like to receive notifications.
3. Click the Actions menu and choose **Manage subscriptions**.
4. Add the subscription for "New security alert raised".
Members of that group will be alerted in two ways:
* Immediately via an email when a new critical finding is discovered
* A banner in the SonarQube interface when a critical finding is present
---
# Agent Instructions
This documentation is published with GitBook. GitBook is the documentation platform designed so that both humans and AI agents can read, navigate, and reason over technical content effectively. Learn more at gitbook.com.
## Querying This Documentation
If you need additional information that is not directly available in this page, you can query the documentation by asking a question.
Perform an HTTP GET request on the following URL with the `ask` and `goal` query parameters:
```
GET https://docs.sonarsource.com/sonarqube-server/user-guide/security-alerts.md?ask=&goal=
```
`ask` is the immediate question: it should be specific, self-contained, and written in natural language.
`goal` is what the user is ultimately trying to achieve, the reason they need the answer. Sharing it helps GitBook give you a better, more relevant answer. A goal is most helpful when it describes the outcome the user wants rather than restating the question. For example, with `ask=how do I create an API token`, a goal like `automate deployments from our CI pipeline` lets GitBook tailor the answer to that use case.
The response will contain a direct answer to the question and relevant excerpts and sources from the documentation.
Use this mechanism when the answer is not explicitly present in the current page, you need clarification or additional context, or you want to retrieve related documentation sections.